Thanks to built-in security and our comprehensive cybersecurity portfolio, Omnivise T3000 is ideally suited to help operators protect their plant.
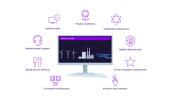
The defense-in-depth concept strengthens your system to withstand external attacks. Omnivise T3000 is certified by TÜV SÜD according to IEC 62443, the leading standard for IT security for industrial communication networks, and is built for Security Level 3 (SL 3) readiness – the level designed for environments exposed to sophisticated, intentional attacks. This is just one example of the numerous internationally recognized standards for which the Omnivise T3000 system as well as our development process is certified for.
We provide long-term support so you can rely on a system that is always up-to-date. We support current hardware on a long-term basis and provide tried and tested security patches for the software at any time during operation. Built-in backup and restore capabilities add another layer of resilience, helping you recover quickly should an incident occur. For you, this means long-term security – with no downtime. In addition, our Cybersecurity Operations Center (cSOC) helps you defend against or resolve cyberattacks 24/7.
We have always shared security announcements and advisories openly, keeping operators informed. This transparency now extends beyond service contract customers: through Customer Energy Portal (CEP) onboarding, every Omnivise T3000 operator gains access to the same security information. If you suspect an actively exploited vulnerability or a severe incident, simply report it to us – we verify it and take care of the necessary next steps. As with IEC 62443 and SL 3, we take the same standards-first approach with Release 10.2 toward the EU Cyber Resilience Act (CRA), embedding and onboarding the modules and features needed for CRA conformity.